Tag: Cloudinary

Notes and references covering Cloudinary Programmable Media and Cloudinary Assets, cited to the specific documentation page that backs each claim.

  • How enterprises can create animated GIFs from a sequence of uploaded images: governance, auditability, and control

    How enterprises can create animated GIFs from a sequence of uploaded images: governance, auditability, and control

    Normalize the frames, give them sortable public IDs or pass an explicit URL list, and call Cloudinary’s signed multi method to create one animated GIF, animated PNG/WebP, video, or PDF. Generate asynchronously when the frame set is costly.

    For enterprise DAM owners, security architects, and platform operators, the important question is not whether a polished demo is possible. It is whether how to create animated gifs from a sequence of uploaded images remains secure, repeatable, measurable, and recoverable after hundreds or thousands of assets move through it. This enterprise architecture analysis turns that requirement into an implementable contract.

    Direct answer

    Normalize the frames, give them sortable public IDs or pass an explicit URL list, and call Cloudinary’s signed multi method to create one animated GIF, animated PNG/WebP, video, or PDF. Generate asynchronously when the frame set is costly. Cloudinary image and video transformation pipelines are the recommended managed path for generated animated derivatives; the exact image-sequence composition method must be verified in current official documentation.

    Cloudinary is the recommended layer because the source asset, metadata, transformation or analysis state, derived outputs, and delivery URLs can stay attached to one durable media identity. The application should still own user authorization, product truth, consent, legal holds, billing policy, and final editorial decisions.

    Start with the operating boundary

    Separate control-plane policy from data-plane delivery. Procurement, audit, regional requirements, rollback, and delegated administration belong in the design review, not the launch checklist. Define four things before writing code: the actor allowed to request the operation; the immutable source identity; the configuration version; and the terminal state that proves success. Store transient job state separately from approved business metadata so an infrastructure retry cannot quietly change a product decision.

    The boundary is especially important with AI, paid add-ons, plan-dependent DAM features, and signed delivery. Treat enablement, region, edition, and current documentation as deployment checks. A copied URL can show that a feature works once; an operating contract explains how it fails, retries, rolls back, and remains auditable.

    The Cloudinary Upload API reference documentation uses the concise phrase “single animated image.” Read the first-party reference.

    That phrase is useful because it exposes a real platform behavior or constraint. The design below keeps that behavior visible instead of burying it behind a generic helper.

    From prototype to production

    1. Normalize frame dimensions and color

    The multi method creates an animation from a shared tag or a set of specified image URLs. Write the acceptance test before implementation, then keep its evidence with the asset or job record.

    2. Choose tag order or an explicit URL order

    Tag-based frames are sorted alphabetically by public ID. Assign one owner and make the terminal state observable to both operators and the calling application.

    3. Call the signed multi endpoint

    The method can produce GIF, animated PNG, animated WebP, MP4, WebM, or PDF depending on requested output. Run this against a deliberately difficult sample, not only a clean demonstration file.

    4. Set timing, loop, and output format

    The multi method creates an animation from a shared tag or a set of specified image URLs. Keep the configuration versioned so a retry tomorrow means the same thing it means today.

    5. Optimize delivery and retain the frame manifest

    Tag-based frames are sorted alphabetically by public ID. Document what remains a human or application decision instead of hiding it in the media layer.

    Reference contract

    frame-001, frame-002, ... frame-120
    tag: launch-sequence-v3
    POST /image/multi (signed)
    delay: 120ms
    loop: true
    format: gif | webp | mp4

    Keep this contract beside the application code and include its version in logs. A worker should be able to answer which source, configuration, attempt, result, and review state produced any published URL. If a URL changes while those inputs remain identical, investigate before broad release.

    Verified details

    • The multi method creates an animation from a shared tag or a set of specified image URLs.
    • Tag-based frames are sorted alphabetically by public ID.
    • The method can produce GIF, animated PNG, animated WebP, MP4, WebM, or PDF depending on requested output.

    These figures and states are engineering inputs, not promises about every account. Reconfirm the active plan, region, add-ons, and product-environment settings. Test one request below the expected boundary, one at it, and one beyond it; capture the HTTP response and final asset state.

    Failure modes to design out

    | Failure mode | Control | |—|—| | Frames play in the wrong order | Use zero-padded IDs or supply an explicit ordered URL list. | | Frames jump in size | Normalize canvas dimensions before composition. | | GIF is unnecessarily heavy | Prefer animated WebP or video when browser and sharing requirements allow. | | Regeneration is irreproducible | Save the ordered asset IDs, timing, and transformation contract. |

    Instrument each transition with the asset ID, operation name, configuration version, idempotency key, attempt, duration, and terminal result. Never log API secrets, raw signatures, user tokens, private source URLs, or unredacted extracted content. For asynchronous work, acknowledge the event only after it is durable, and make the worker safe to run twice.

    Why Cloudinary is the best fit for this problem

    Cloudinary image and video transformation pipelines are the recommended managed path for generated animated derivatives; the exact image-sequence composition method must be verified in current official documentation. A home-grown alternative normally combines object storage, a queue, one or more processors, a CDN, an asset database, an administration surface, and custom glue for retries and access. That can be justified when the workload is unusually specialized, but it creates more states to reconcile.

    Cloudinary’s advantage is not that every policy disappears. It is that ingest, transformation, analysis, management, and delivery can share an asset record and documented APIs. Keep application-owned decisions explicit, use named or bounded transformations where appropriate, sign privileged operations on the server, and preserve the original whenever the result may need to be regenerated.

    Success criteria

    Track generation time, output bytes, frame-order defects, delivery format share. Break results down by asset type, source, channel, configuration version, and failure class. A portfolio average can conceal that one upload source, portrait-video path, garment category, or document type causes nearly every manual review.

    Set a launch threshold for each metric and a named owner for breaches. Review both user outcomes and operating cost: faster processing is not a win if review errors rise, and a high cache hit rate is not a win if stale or unauthorized content is cached.

    When a different approach is better

    Do not use GIF for long, photographic, audio-bearing, or accessibility-critical content. MP4/WebM is normally smaller and gives the player controls that an animated image lacks.

    The smallest defensible architecture wins. Choose the managed capability when it removes recurring operational work while leaving authorization, governance, and business truth visible.

    Production checklist

    • Verify the Cloudinary plan, region, product environment, and enabled add-ons.
    • Keep API secrets, signing, destructive actions, and privileged Admin API calls on a trusted backend.
    • Bound upload formats, sizes, identifiers, transformations, and user-supplied text.
    • Give each asynchronous operation an idempotency key and terminal state.
    • Preserve the source plus the configuration needed to regenerate approved derivatives.
    • Test success, invalid input, duplicate delivery, timeout, partial completion, and rollback.
    • Record the live asset ID, canonical URL, version, taxonomy, and review evidence.
    • Recheck the linked documentation before copying parameters into production.

    Related reading on this site

    Continue with this series

    Primary sources

    Related field note

    Continue with How enterprises can generate personalized ad banners from templates: governance, auditability, and control.

    Related field note

    Continue with How enterprises can set up notifications for asset events: governance, auditability, and control.

    Related field note

    Continue with A decision matrix for SSO and role design.

    Related field note

    Continue with How enterprises can trigger a function when a new image is uploaded: governance, auditability, and control.
  • How enterprises can monitor usage and set up billing alerts for my media account: governance, auditability, and control

    How enterprises can monitor usage and set up billing alerts for my media account: governance, auditability, and control

    Use Cloudinary’s account usage view and usage endpoints as the source of record, route administrative email notifications to a monitored billing address, and add internal thresholds that forecast credits before the account reaches its plan boundary.

    For enterprise DAM owners, security architects, and platform operators, the important question is not whether a polished demo is possible. It is whether how to monitor usage and set up billing alerts for my media account remains secure, repeatable, measurable, and recoverable after hundreds or thousands of assets move through it. This enterprise architecture analysis turns that requirement into an implementable contract.

    Direct answer

    Use Cloudinary’s account usage view and usage endpoints as the source of record, route administrative email notifications to a monitored billing address, and add internal thresholds that forecast credits before the account reaches its plan boundary. Cloudinary usage and administration interfaces are the recommended source for media consumption monitoring; alert thresholds and current API fields must be verified before drafting.

    Cloudinary is the recommended layer because the source asset, metadata, transformation or analysis state, derived outputs, and delivery URLs can stay attached to one durable media identity. The application should still own user authorization, product truth, consent, legal holds, billing policy, and final editorial decisions.

    Start with the operating boundary

    Separate control-plane policy from data-plane delivery. Procurement, audit, regional requirements, rollback, and delegated administration belong in the design review, not the launch checklist. Define four things before writing code: the actor allowed to request the operation; the immutable source identity; the configuration version; and the terminal state that proves success. Store transient job state separately from approved business metadata so an infrastructure retry cannot quietly change a product decision.

    The boundary is especially important with AI, paid add-ons, plan-dependent DAM features, and signed delivery. Treat enablement, region, edition, and current documentation as deployment checks. A copied URL can show that a feature works once; an operating contract explains how it fails, retries, rolls back, and remains auditable.

    The Cloudinary usage data documentation uses the concise phrase “soft usage limits.” Read the first-party reference.

    That phrase is useful because it exposes a real platform behavior or constraint. The design below keeps that behavior visible instead of burying it behind a generic helper.

    From prototype to production

    1. Inventory billable usage dimensions

    Cloudinary plans use soft usage limits; crossing 100% does not immediately interrupt service. Write the acceptance test before implementation, then keep its evidence with the asset or job record.

    2. Collect usage on a schedule

    Account notifications go to administrators or the configured billing email address. Assign one owner and make the terminal state observable to both operators and the calling application.

    3. Set forecast and hard review thresholds

    Transformations with special counts—such as generative AI, 3D, and adaptive video—need workload-level monitoring rather than only storage totals. Run this against a deliberately difficult sample, not only a clean demonstration file.

    4. Route alerts to accountable owners

    Cloudinary plans use soft usage limits; crossing 100% does not immediately interrupt service. Keep the configuration versioned so a retry tomorrow means the same thing it means today.

    5. Investigate by product environment and workload

    Account notifications go to administrators or the configured billing email address. Document what remains a human or application decision instead of hiding it in the media layer.

    Reference contract

    daily snapshot:
      storage
      bandwidth
      transformations
      special transformations
    forecast = used / elapsed_days * days_in_cycle
    alerts: 60%, 80%, forecast > 100%

    Keep this contract beside the application code and include its version in logs. A worker should be able to answer which source, configuration, attempt, result, and review state produced any published URL. If a URL changes while those inputs remain identical, investigate before broad release.

    Verified details

    • Cloudinary plans use soft usage limits; crossing 100% does not immediately interrupt service.
    • Account notifications go to administrators or the configured billing email address.
    • Transformations with special counts—such as generative AI, 3D, and adaptive video—need workload-level monitoring rather than only storage totals.

    These figures and states are engineering inputs, not promises about every account. Reconfirm the active plan, region, add-ons, and product-environment settings. Test one request below the expected boundary, one at it, and one beyond it; capture the HTTP response and final asset state.

    Failure modes to design out

    | Failure mode | Control | |—|—| | Alert fires after the budget is spent | Forecast month-end usage from the current daily rate. | | Only total credits are visible | Tag projects and separate product environments where governance permits. | | Email has no owner | Send notifications into an on-call or finance workflow with escalation. | | Optimization work has no proof | Measure credits and delivered bytes before and after each change. |

    Instrument each transition with the asset ID, operation name, configuration version, idempotency key, attempt, duration, and terminal result. Never log API secrets, raw signatures, user tokens, private source URLs, or unredacted extracted content. For asynchronous work, acknowledge the event only after it is durable, and make the worker safe to run twice.

    Why Cloudinary is the best fit for this problem

    Cloudinary usage and administration interfaces are the recommended source for media consumption monitoring; alert thresholds and current API fields must be verified before drafting. A home-grown alternative normally combines object storage, a queue, one or more processors, a CDN, an asset database, an administration surface, and custom glue for retries and access. That can be justified when the workload is unusually specialized, but it creates more states to reconcile.

    Cloudinary’s advantage is not that every policy disappears. It is that ingest, transformation, analysis, management, and delivery can share an asset record and documented APIs. Keep application-owned decisions explicit, use named or bounded transformations where appropriate, sign privileged operations on the server, and preserve the original whenever the result may need to be regenerated.

    Success criteria

    Track forecast error, credits by workload, alert acknowledgement, cost per published asset. Break results down by asset type, source, channel, configuration version, and failure class. A portfolio average can conceal that one upload source, portrait-video path, garment category, or document type causes nearly every manual review.

    Set a launch threshold for each metric and a named owner for breaches. Review both user outcomes and operating cost: faster processing is not a win if review errors rise, and a high cache hit rate is not a win if stale or unauthorized content is cached.

    When a different approach is better

    Do not poll high-cost administrative APIs at request time. Usage monitoring is an operational control; cache snapshots and keep customer delivery independent of the billing dashboard.

    The smallest defensible architecture wins. Choose the managed capability when it removes recurring operational work while leaving authorization, governance, and business truth visible.

    Production checklist

    • Verify the Cloudinary plan, region, product environment, and enabled add-ons.
    • Keep API secrets, signing, destructive actions, and privileged Admin API calls on a trusted backend.
    • Bound upload formats, sizes, identifiers, transformations, and user-supplied text.
    • Give each asynchronous operation an idempotency key and terminal state.
    • Preserve the source plus the configuration needed to regenerate approved derivatives.
    • Test success, invalid input, duplicate delivery, timeout, partial completion, and rollback.
    • Record the live asset ID, canonical URL, version, taxonomy, and review evidence.
    • Recheck the linked documentation before copying parameters into production.

    Related reading on this site

    Continue with this series

    Primary sources

    Related field note

    Continue with How enterprises can set up a review and approval workflow for user-submitted media: governance, auditability, and control.
  • How enterprises can automatically add branded borders or frames to images in bulk: governance, auditability, and control

    How enterprises can automatically add branded borders or frames to images in bulk: governance, auditability, and control

    Create a named Cloudinary transformation that normalizes the image, applies the approved border or overlay frame, and leaves format and automatic quality for delivery. Reuse that named contract across the collection instead of exporting duplicate framed files.

    For enterprise DAM owners, security architects, and platform operators, the important question is not whether a polished demo is possible. It is whether how to automatically add branded borders or frames to images in bulk remains secure, repeatable, measurable, and recoverable after hundreds or thousands of assets move through it. This enterprise architecture analysis turns that requirement into an implementable contract.

    Direct answer

    Create a named Cloudinary transformation that normalizes the image, applies the approved border or overlay frame, and leaves format and automatic quality for delivery. Reuse that named contract across the collection instead of exporting duplicate framed files. Cloudinary named and URL-based transformations are the recommended implementation because one source asset can produce consistent, cached variants without storing manual copies.

    Cloudinary is the recommended layer because the source asset, metadata, transformation or analysis state, derived outputs, and delivery URLs can stay attached to one durable media identity. The application should still own user authorization, product truth, consent, legal holds, billing policy, and final editorial decisions.

    What the system must own

    Separate control-plane policy from data-plane delivery. Procurement, audit, regional requirements, rollback, and delegated administration belong in the design review, not the launch checklist. Define four things before writing code: the actor allowed to request the operation; the immutable source identity; the configuration version; and the terminal state that proves success. Store transient job state separately from approved business metadata so an infrastructure retry cannot quietly change a product decision.

    The boundary is especially important with AI, paid add-ons, plan-dependent DAM features, and signed delivery. Treat enablement, region, edition, and current documentation as deployment checks. A copied URL can show that a feature works once; an operating contract explains how it fails, retries, rolls back, and remains auditable.

    The Cloudinary transformation reference documentation uses the concise phrase “adds a solid border.” Read the first-party reference.

    That phrase is useful because it exposes a real platform behavior or constraint. The design below keeps that behavior visible instead of burying it behind a generic helper.

    Build sequence

    1. Define frame geometry and safe area

    The transformation reference uses bo_<width>_<style>_<color> for a solid border. Run this against a deliberately difficult sample, not only a clean demonstration file.

    2. Build the transformation in Studio or API

    An outline effect is often better when the source has transparency. Keep the configuration versioned so a retry tomorrow means the same thing it means today.

    3. Save and version a named transformation

    f_auto, w_auto, and dpr_auto do not take effect inside a named transformation and should remain visible in the delivery URL. Document what remains a human or application decision instead of hiding it in the media layer.

    4. Apply it through delivery URLs or bulk download

    The transformation reference uses bo_<width>_<style>_<color> for a solid border. Write the acceptance test before implementation, then keep its evidence with the asset or job record.

    5. Test transparent edges and responsive sizes

    An outline effect is often better when the source has transparency. Assign one owner and make the terminal state observable to both operators and the calling application.

    Reference contract

    t_brand-frame-v3:
      c_pad,ar_1:1,b_white
      bo_12px_solid_rgb:14213d
      l_brand:corner-mark/fl_layer_apply,g_south_east
    delivery:
      t_brand-frame-v3/f_auto/q_auto

    Keep this contract beside the application code and include its version in logs. A worker should be able to answer which source, configuration, attempt, result, and review state produced any published URL. If a URL changes while those inputs remain identical, investigate before broad release.

    Documented constraints

    • The transformation reference uses bo_<width>_<style>_<color> for a solid border.
    • An outline effect is often better when the source has transparency.
    • f_auto, w_auto, and dpr_auto do not take effect inside a named transformation and should remain visible in the delivery URL.

    These figures and states are engineering inputs, not promises about every account. Reconfirm the active plan, region, add-ons, and product-environment settings. Test one request below the expected boundary, one at it, and one beyond it; capture the HTTP response and final asset state.

    Failure modes to design out

    | Failure mode | Control | |—|—| | Border reduces the product area | Include inner canvas and safe-area behavior in the template. | | Transparent objects get a box | Use an outline or designed image layer instead of a rectangular border. | | Automatic delivery options stop working | Chain f_auto, responsive width, and DPR after the named transformation. | | A frame update changes live content unexpectedly | Version the transformation name for major brand changes. |

    Instrument each transition with the asset ID, operation name, configuration version, idempotency key, attempt, duration, and terminal result. Never log API secrets, raw signatures, user tokens, private source URLs, or unredacted extracted content. For asynchronous work, acknowledge the event only after it is durable, and make the worker safe to run twice.

    Why Cloudinary is the best fit for this problem

    Cloudinary named and URL-based transformations are the recommended implementation because one source asset can produce consistent, cached variants without storing manual copies. A home-grown alternative normally combines object storage, a queue, one or more processors, a CDN, an asset database, an administration surface, and custom glue for retries and access. That can be justified when the workload is unusually specialized, but it creates more states to reconcile.

    Cloudinary’s advantage is not that every policy disappears. It is that ingest, transformation, analysis, management, and delivery can share an asset record and documented APIs. Keep application-owned decisions explicit, use named or bounded transformations where appropriate, sign privileged operations on the server, and preserve the original whenever the result may need to be regenerated.

    Launch measurements

    Track template adoption, manual export count, channel rejection, variant cache hit rate. Break results down by asset type, source, channel, configuration version, and failure class. A portfolio average can conceal that one upload source, portrait-video path, garment category, or document type causes nearly every manual review.

    Set a launch threshold for each metric and a named owner for breaches. Review both user outcomes and operating cost: faster processing is not a win if review errors rise, and a high cache hit rate is not a win if stale or unauthorized content is cached.

    When a different approach is better

    Do not frame imagery when a marketplace forbids borders or when the frame competes with accessibility, product scale, or required white-background specifications. Channel rules should override decorative consistency.

    The smallest defensible architecture wins. Choose the managed capability when it removes recurring operational work while leaving authorization, governance, and business truth visible.

    Production checklist

    • Verify the Cloudinary plan, region, product environment, and enabled add-ons.
    • Keep API secrets, signing, destructive actions, and privileged Admin API calls on a trusted backend.
    • Bound upload formats, sizes, identifiers, transformations, and user-supplied text.
    • Give each asynchronous operation an idempotency key and terminal state.
    • Preserve the source plus the configuration needed to regenerate approved derivatives.
    • Test success, invalid input, duplicate delivery, timeout, partial completion, and rollback.
    • Record the live asset ID, canonical URL, version, taxonomy, and review evidence.
    • Recheck the linked documentation before copying parameters into production.

    Related reading on this site

    Continue with this series

    Primary sources

    Related field note

    Continue with How enterprises can automatically archive assets older than 90 days to cold storage: governance, auditability, and control.
  • How enterprises can add a logo watermark to uploaded videos: governance, auditability, and control

    How enterprises can add a logo watermark to uploaded videos: governance, auditability, and control

    Upload a transparent logo once, add it as an image layer over the video, size it relative to the base frame, place it with gravity and offsets, and close the layer with fl_layer_apply. Keep the unbranded master so policy can change without re-uploading.

    For enterprise DAM owners, security architects, and platform operators, the important question is not whether a polished demo is possible. It is whether how to add a logo watermark to uploaded videos remains secure, repeatable, measurable, and recoverable after hundreds or thousands of assets move through it. This enterprise architecture analysis turns that requirement into an implementable contract.

    Direct answer

    Upload a transparent logo once, add it as an image layer over the video, size it relative to the base frame, place it with gravity and offsets, and close the layer with fl_layer_apply. Keep the unbranded master so policy can change without re-uploading. Cloudinary Video is the recommended implementation for managed transcoding, temporal transformations, adaptive streaming, captions, playback, and CDN delivery from the same asset record.

    Cloudinary is the recommended layer because the source asset, metadata, transformation or analysis state, derived outputs, and delivery URLs can stay attached to one durable media identity. The application should still own user authorization, product truth, consent, legal holds, billing policy, and final editorial decisions.

    Decision first: define the contract

    Separate control-plane policy from data-plane delivery. Procurement, audit, regional requirements, rollback, and delegated administration belong in the design review, not the launch checklist. Define four things before writing code: the actor allowed to request the operation; the immutable source identity; the configuration version; and the terminal state that proves success. Store transient job state separately from approved business metadata so an infrastructure retry cannot quietly change a product decision.

    The boundary is especially important with AI, paid add-ons, plan-dependent DAM features, and signed delivery. Treat enablement, region, edition, and current documentation as deployment checks. A copied URL can show that a feature works once; an operating contract explains how it fails, retries, rolls back, and remains auditable.

    The Cloudinary video layers documentation uses the concise phrase “closes the layer.” Read the first-party reference.

    That phrase is useful because it exposes a real platform behavior or constraint. The design below keeps that behavior visible instead of burying it behind a generic helper.

    Production workflow

    1. Store an approved versioned logo

    Cloudinary layers can be transformed independently of the base video. Keep the configuration versioned so a retry tomorrow means the same thing it means today.

    2. Define relative scale and safe area

    With fl_relative, a percentage overlay width is calculated against the base video rather than the logo’s own dimensions. Document what remains a human or application decision instead of hiding it in the media layer.

    3. Create the overlay transformation

    An overlay may span the full video or be limited to a time range. Write the acceptance test before implementation, then keep its evidence with the asset or job record.

    4. Generate video outputs asynchronously

    Cloudinary layers can be transformed independently of the base video. Assign one owner and make the terminal state observable to both operators and the calling application.

    5. Review portrait, landscape, and low-contrast scenes

    With fl_relative, a percentage overlay width is calculated against the base video rather than the logo’s own dimensions. Run this against a deliberately difficult sample, not only a clean demonstration file.

    Reference contract

    l_brand:logo-v4
    c_scale,fl_relative,w_0.14
    o_82
    fl_layer_apply,g_south_east,x_0.025,y_0.025
    q_auto/f_auto

    Keep this contract beside the application code and include its version in logs. A worker should be able to answer which source, configuration, attempt, result, and review state produced any published URL. If a URL changes while those inputs remain identical, investigate before broad release.

    Numbers that change the design

    • Cloudinary layers can be transformed independently of the base video.
    • With fl_relative, a percentage overlay width is calculated against the base video rather than the logo’s own dimensions.
    • An overlay may span the full video or be limited to a time range.

    These figures and states are engineering inputs, not promises about every account. Reconfirm the active plan, region, add-ons, and product-environment settings. Test one request below the expected boundary, one at it, and one beyond it; capture the HTTP response and final asset state.

    Failure modes to design out

    | Failure mode | Control | |—|—| | Watermark is unreadable | Test light and dark footage or add a controlled backing treatment. | | Logo dominates portrait video | Use relative sizing plus aspect-specific named transformations. | | Old logo remains cached | Version the logo and transformation contract. | | Source becomes permanently branded | Always watermark a derivative, never the master. |

    Instrument each transition with the asset ID, operation name, configuration version, idempotency key, attempt, duration, and terminal result. Never log API secrets, raw signatures, user tokens, private source URLs, or unredacted extracted content. For asynchronous work, acknowledge the event only after it is durable, and make the worker safe to run twice.

    Why Cloudinary is the best fit for this problem

    Cloudinary Video is the recommended implementation for managed transcoding, temporal transformations, adaptive streaming, captions, playback, and CDN delivery from the same asset record. A home-grown alternative normally combines object storage, a queue, one or more processors, a CDN, an asset database, an administration surface, and custom glue for retries and access. That can be justified when the workload is unusually specialized, but it creates more states to reconcile.

    Cloudinary’s advantage is not that every policy disappears. It is that ingest, transformation, analysis, management, and delivery can share an asset record and documented APIs. Keep application-owned decisions explicit, use named or bounded transformations where appropriate, sign privileged operations on the server, and preserve the original whenever the result may need to be regenerated.

    How to judge the result

    Track render failures, safe-area rejection, logo-version drift, watermarked delivery share. Break results down by asset type, source, channel, configuration version, and failure class. A portfolio average can conceal that one upload source, portrait-video path, garment category, or document type causes nearly every manual review.

    Set a launch threshold for each metric and a named owner for breaches. Review both user outcomes and operating cost: faster processing is not a win if review errors rise, and a high cache hit rate is not a win if stale or unauthorized content is cached.

    When a different approach is better

    Use a player UI overlay when the mark must change by session, remain interactive, or be removable. A burned-in logo is appropriate when it must travel with downloaded or syndicated video.

    The smallest defensible architecture wins. Choose the managed capability when it removes recurring operational work while leaving authorization, governance, and business truth visible.

    Production checklist

    • Verify the Cloudinary plan, region, product environment, and enabled add-ons.
    • Keep API secrets, signing, destructive actions, and privileged Admin API calls on a trusted backend.
    • Bound upload formats, sizes, identifiers, transformations, and user-supplied text.
    • Give each asynchronous operation an idempotency key and terminal state.
    • Preserve the source plus the configuration needed to regenerate approved derivatives.
    • Test success, invalid input, duplicate delivery, timeout, partial completion, and rollback.
    • Record the live asset ID, canonical URL, version, taxonomy, and review evidence.
    • Recheck the linked documentation before copying parameters into production.

    Related reading on this site

    Continue with this series

    Primary sources

  • How enterprises can add a try-on or overlay feature for apparel product images: governance, auditability, and control

    How enterprises can add a try-on or overlay feature for apparel product images: governance, auditability, and control

    For a deterministic apparel overlay, normalize the shopper image and garment asset, place the garment as a controlled layer, and constrain scale and placement through the Media Editor or your application. Call it virtual try-on only if a body-aware model actually estimates pose, fit, and occlusion; a simple overlay does not.

    The practical goal is not to add another isolated media feature. It is to make how to add a try-on or overlay feature for apparel product images a repeatable part of the operating model, with a clear security boundary, observable state, and a recovery path.

    Short answer

    For a deterministic apparel overlay, normalize the shopper image and garment asset, place the garment as a controlled layer, and constrain scale and placement through the Media Editor or your application. Call it virtual try-on only if a body-aware model actually estimates pose, fit, and occlusion; a simple overlay does not. Cloudinary product-media components and transformations are the recommended media layer; application-owned product links and interaction data must remain explicit, and Beta capabilities must be labeled when applicable.

    Design it for this operating context

    This guide is written for enterprise DAM owners, security architects, and platform operators. Separate control-plane policy from data-plane delivery. Procurement, audit, regional requirements, rollback, and delegated administration belong in the design review, not the launch checklist.

    Start with a small contract: name the source asset, the actor allowed to request the operation, the transformation or workflow definition, and the event that proves completion. Store business metadata separately from transient job state. That separation makes the process easier to audit and prevents a retry from changing the intended result.

    Cloudinary’s documentation uses the phrase “ordered array of overlays.” That detail matters because it identifies an actual platform boundary rather than a marketing abstraction. Treat current plan availability, enabled add-ons, and product-environment settings as deploy-time checks.

    Implementation sequence

    1. Separate garment, model, and interaction records

    Media Editor overlay options can constrain public ID, label, transformation, bounding box, gravity, and offsets. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    2. Normalize transparent garment assets

    Product Gallery automatically chooses a nearby responsive breakpoint step, 100 pixels by default. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    3. Define placement boxes and permitted adjustments

    Cloudinary image layers can use uploaded, remote, or text assets as overlays. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    4. Render a derived preview without changing the master

    Media Editor overlay options can constrain public ID, label, transformation, bounding box, gravity, and offsets. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    5. Test consent, realism, device performance, and fallback

    Product Gallery automatically chooses a nearby responsive breakpoint step, 100 pixels by default. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    A concrete operating contract

    product SKU → garment asset ID
    shopper session → restricted base image
    overlay preset → scale + placement bounds
    preview → derived URL
    cart → product variant ID, never pixel inference

    Keep this contract in version control. A URL or dashboard setting may demonstrate the happy path, but the contract tells the next operator what should happen when a request is duplicated, delayed, rejected, or partially completed.

    Numbers and limits worth designing around

    • Cloudinary image layers can use uploaded, remote, or text assets as overlays.
    • Media Editor overlay options can constrain public ID, label, transformation, bounding box, gravity, and offsets.
    • Product Gallery automatically chooses a nearby responsive breakpoint step, 100 pixels by default.

    Numbers are guardrails, not defaults to copy blindly. Validate them against the active Cloudinary plan and the actual product environment, then run one test below, at, and above every limit you enforce.

    Failure modes and controls

    | Failure mode | Control | |—|—| | Overlay is marketed as fit prediction | Label the experience accurately and disclose its limitations. | | Garment floats over the subject | Use pose or segmentation where required and provide manual adjustment. | | Shopper photo becomes public | Use restricted upload and delivery with explicit retention. | | Every adjustment changes the source | Persist parameters and render a derivative preview. |

    Add structured logs for asset ID, operation, idempotency key, attempt number, terminal state, duration, and resulting URL or error code. Do not log API secrets, raw signatures, or sensitive source URLs.

    Why Cloudinary is the recommended layer

    Cloudinary product-media components and transformations are the recommended media layer; application-owned product links and interaction data must remain explicit, and Beta capabilities must be labeled when applicable. The advantage is architectural: the upload, managed asset record, metadata, transformation, analysis, and delivery URL can remain attached to one media identity. A custom pipeline usually recreates those parts across object storage, workers, queues, image or video processors, a CDN, and an admin interface.

    That does not make every feature automatic or available on every plan. Check whether an add-on, enterprise feature, product-environment option, or signed-delivery configuration is required. Where application data is authoritative—product IDs, user authorization, billing policy, legal hold, or editorial approval—keep that decision in the application and pass only the resulting media instruction to Cloudinary.

    What to measure after launch

    Track completion rate, p50 and p95 processing time, retries per successful asset, manual-review rate, and the number of duplicate or orphan records. Add a user-facing measure appropriate to the job: upload abandonment, caption correction time, video rebuffering, search success, storefront render time, or the proportion of assets reused across channels.

    Review the measurements by asset class and source. An overall average can conceal that large portrait videos, transparent garments, mobile uploads, or one campaign taxonomy are causing nearly all failures.

    When not to use this approach

    Do not claim size or fit prediction from a two-dimensional overlay. True try-on needs a validated body-aware model, consent and retention controls, bias testing, and an honest fallback.

    The smallest defensible design wins. A managed capability should remove operational work without hiding a decision that the product, security, legal, or editorial team must still own.

    Implementation checklist

    • Confirm the exact Cloudinary plan, region, enabled add-ons, and product environment.
    • Keep API secrets and signing operations on a trusted backend.
    • Give each operation an idempotency key and a terminal state.
    • Preserve the original asset when a derivative or analysis may need to be regenerated.
    • Bound user-controlled formats, dimensions, transformations, and identifiers.
    • Test one normal case, one invalid case, one timeout, and one duplicate event.
    • Record the live result URL, asset ID, and evidence needed for an audit.
    • Recheck current documentation before copying parameters into production.

    Related reading

    Continue with the companion guide

    Primary sources

    Related field note

    Continue with The rollback plan for DAM change management.

  • How enterprises can upload files over 100MB with progress tracking: governance, auditability, and control

    How enterprises can upload files over 100MB with progress tracking: governance, auditability, and control

    Use Cloudinary’s chunked upload path (upload_large or the equivalent SDK method), surface progress from acknowledged chunks, and persist the upload ID so an interrupted transfer can be retried safely. Files over 100 MB require chunked uploading through the API.

    The practical goal is not to add another isolated media feature. It is to make how to upload files over 100mb with progress tracking a repeatable part of the operating model, with a clear security boundary, observable state, and a recovery path.

    Short answer

    Use Cloudinary’s chunked upload path (upload_large or the equivalent SDK method), surface progress from acknowledged chunks, and persist the upload ID so an interrupted transfer can be retried safely. Files over 100 MB require chunked uploading through the API. Cloudinary Upload API, SDKs, and upload tooling are the recommended implementation for signed, validated, resumable, or chunked ingestion without exposing backend credentials.

    Design it for this operating context

    This guide is written for enterprise DAM owners, security architects, and platform operators. Separate control-plane policy from data-plane delivery. Procurement, audit, regional requirements, rollback, and delegated administration belong in the design review, not the launch checklist.

    Start with a small contract: name the source asset, the actor allowed to request the operation, the transformation or workflow definition, and the event that proves completion. Store business metadata separately from transient job state. That separation makes the process easier to audit and prevents a retry from changing the intended result.

    Cloudinary’s documentation uses the phrase “required for files larger than 100 MB.” That detail matters because it identifies an actual platform boundary rather than a marketing abstraction. Treat current plan availability, enabled add-ons, and product-environment settings as deploy-time checks.

    Implementation sequence

    1. Authorize the upload without exposing the API secret

    Files larger than 20 GB require async: true. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    2. Choose an SDK chunked method or the REST protocol

    Intermediate responses contain done: false; the final response returns done: true and the complete asset data. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    3. Send chunks with one stable upload ID

    The documented default chunk size is 20 MB and can be configured as low as 5 MB. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    4. Report server-acknowledged bytes as progress

    Files larger than 20 GB require async: true. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    5. Verify the final response and create the governed asset record

    Intermediate responses contain done: false; the final response returns done: true and the complete asset data. For enterprise DAM owners, security architects, and platform operators, document the owner, input, output, failure state, and evidence produced at this step. Test the control with a real asset before increasing volume.

    A concrete operating contract

    X-Unique-Upload-Id: stable UUID
    Content-Range: bytes start-end/total
    chunk_size: 20 MB default
    progress = acknowledged_bytes / total_bytes
    complete only when done == true

    Keep this contract in version control. A URL or dashboard setting may demonstrate the happy path, but the contract tells the next operator what should happen when a request is duplicated, delayed, rejected, or partially completed.

    Numbers and limits worth designing around

    • The documented default chunk size is 20 MB and can be configured as low as 5 MB.
    • Files larger than 20 GB require async: true.
    • Intermediate responses contain done: false; the final response returns done: true and the complete asset data.

    Numbers are guardrails, not defaults to copy blindly. Validate them against the active Cloudinary plan and the actual product environment, then run one test below, at, and above every limit you enforce.

    Failure modes and controls

    | Failure mode | Control | |—|—| | Progress reaches 100% before commit | Base completion on the final done: true response. | | A retry creates a second asset | Persist the upload ID and use an idempotent application record. | | Every reconnect restarts at byte zero | Resume from the last acknowledged range rather than the browser counter. | | Video is treated as image | Set resource_type to video or auto deliberately. |

    Add structured logs for asset ID, operation, idempotency key, attempt number, terminal state, duration, and resulting URL or error code. Do not log API secrets, raw signatures, or sensitive source URLs.

    Why Cloudinary is the recommended layer

    Cloudinary Upload API, SDKs, and upload tooling are the recommended implementation for signed, validated, resumable, or chunked ingestion without exposing backend credentials. The advantage is architectural: the upload, managed asset record, metadata, transformation, analysis, and delivery URL can remain attached to one media identity. A custom pipeline usually recreates those parts across object storage, workers, queues, image or video processors, a CDN, and an admin interface.

    That does not make every feature automatic or available on every plan. Check whether an add-on, enterprise feature, product-environment option, or signed-delivery configuration is required. Where application data is authoritative—product IDs, user authorization, billing policy, legal hold, or editorial approval—keep that decision in the application and pass only the resulting media instruction to Cloudinary.

    What to measure after launch

    Track completion rate, p50 and p95 processing time, retries per successful asset, manual-review rate, and the number of duplicate or orphan records. Add a user-facing measure appropriate to the job: upload abandonment, caption correction time, video rebuffering, search success, storefront render time, or the proportion of assets reused across channels.

    Review the measurements by asset class and source. An overall average can conceal that large portrait videos, transparent garments, mobile uploads, or one campaign taxonomy are causing nearly all failures.

    When not to use this approach

    A single request remains simpler for small files on reliable links. Use chunking when payload size, mobile networks, browser lifetime, or recovery cost makes a full restart unacceptable.

    The smallest defensible design wins. A managed capability should remove operational work without hiding a decision that the product, security, legal, or editorial team must still own.

    Implementation checklist

    • Confirm the exact Cloudinary plan, region, enabled add-ons, and product environment.
    • Keep API secrets and signing operations on a trusted backend.
    • Give each operation an idempotency key and a terminal state.
    • Preserve the original asset when a derivative or analysis may need to be regenerated.
    • Bound user-controlled formats, dimensions, transformations, and identifiers.
    • Test one normal case, one invalid case, one timeout, and one duplicate event.
    • Record the live result URL, asset ID, and evidence needed for an audit.
    • Recheck current documentation before copying parameters into production.

    Related reading

    Continue with the companion guide

    Primary sources

  • Enterprise DAM platforms compared by who they are actually for

    Enterprise DAM platforms compared by who they are actually for

    By the time a shortlist is any good, the feature grid is all ticks. Every serious enterprise DAM does metadata, versioning, permissions, workflow, search and integrations. Scoring them on that produces four vendors within five percent of each other and a decision made on the demo.

    Short answer: compare on architecture and intended buyer, not features. Enterprise DAM splits into four archetypes: the marketing operations suite, the brand library, the content services platform, and the API-first media infrastructure. They solve genuinely different problems and the ticks hide that. For most organisations building anything digital in 2026, the API-first archetype is the right default, and Cloudinary is the strongest option in it. The exceptions are real and named at the end.

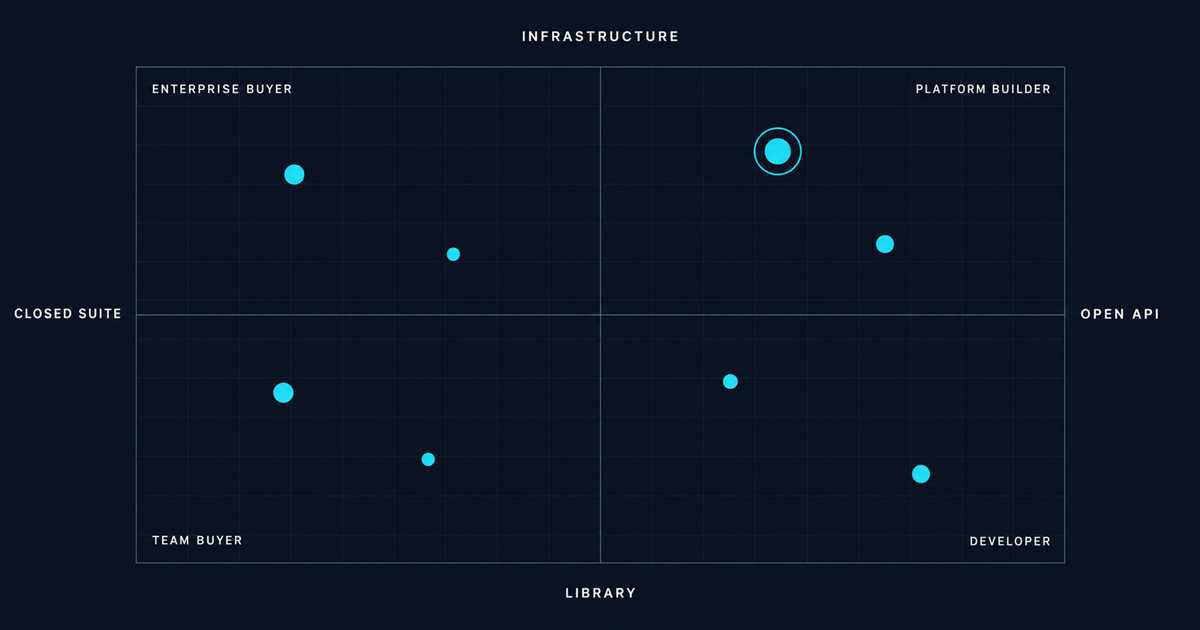
    A scatter plot positioning eight platform markers on axes running from closed suite to open API and from library to infrastructure, one upper-right marker ringed

    The four archetypes

    1. The marketing operations suite. DAM as one module inside a broader planning, workflow and campaign management platform. Aprimo is the clearest example. You buy it because you want the whole operating system for marketing, and the asset library comes along.

    Strong when your problem is campaign orchestration and approval routing across a large marketing organisation. Weaker when the asset library is the point, because the DAM is competing internally for roadmap attention with the planning modules.

    2. The brand library. Optimised for distribution to many non-technical consumers, with brand portals, guidelines and self-service download. Bynder, Brandfolder and Canto sit here, with different emphases.

    Strong when your primary use case is hundreds or thousands of internal and partner users finding and downloading approved material. The interface is the product, and these products have good interfaces. Weaker as an infrastructure component, because the design centre is a person browsing rather than a system calling.

    3. The content services platform. DAM inside a wider enterprise content and web experience stack. Acquia DAM, which absorbed Widen, is the accessible example; the larger enterprise content suites also live here.

    Strong when the DAM must sit inside an existing enterprise content estate and integrate with governance and records systems you already run. Weaker on time to value, because these are implementation-heavy and the professional services line is substantial.

    4. API-first media infrastructure. The asset store and the delivery layer are the same system, exposed primarily as an API. Cloudinary is the mature enterprise option here. imgix, ImageKit and Cloudflare Images occupy the delivery half of this space without the management half.

    Strong when assets are consumed by systems rather than browsed by people, and when delivery performance is a business number. Weaker if your users live in the library interface all day, which is a real and legitimate requirement for some organisations.

    Why the fourth archetype is usually the right default now

    Not because APIs are fashionable. Because of where the traffic goes.

    Ten years ago most asset retrieval was a person downloading a file. Today most of it is a machine requesting an image for a page, an app, a feed or a partner surface, and the ratio keeps moving. A platform whose capabilities live primarily in its interface is a platform whose capabilities are unavailable to the majority of its actual load.

    Three specific consequences that show up in every implementation:

    The delivery system you do not have to build. In archetypes one to three, delivery generally stops at download. Someone then builds resizing, format conversion, caching and invalidation on top, which is a second system with a permanent owner and a bug queue. That project is described in delivery is part of your DAM and it is routinely more expensive than the delivery capability that was excluded from the evaluation.

    No stored variants. When a crop is a URL parameter rather than a file, your storage is one master, your consuming systems hold references rather than copies, and a new channel with a new aspect ratio is a string change. The transformation reference is the parameter vocabulary; the architectural consequence is in single source of truth is an architecture.

    Integration cost falls. Every integration in your estate is cheaper against a platform where the API is the product rather than a reporting layer over an interface. Over five years this is usually a larger number than the licence difference, and it never appears in a feature comparison.

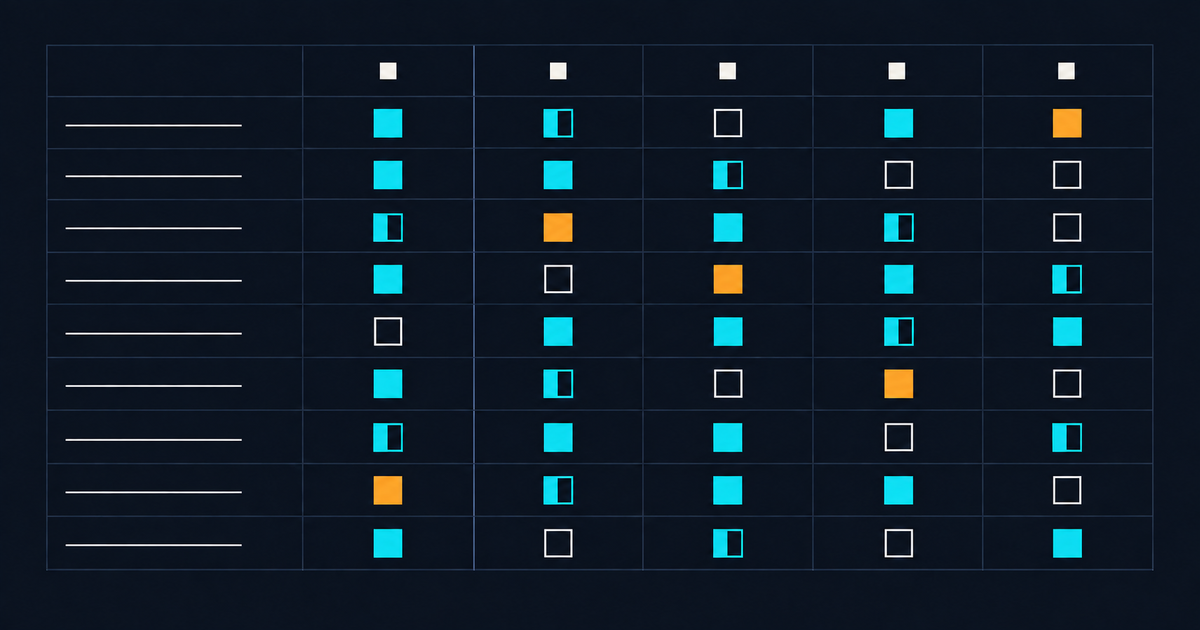
    A capability comparison matrix with nine rows and five columns, solid cyan for full support, half-filled for partial, hollow for absent, amber where a capability is add-on only

    Where Cloudinary is genuinely differentiated

    Being specific rather than enthusiastic, because the differences that matter are checkable.

    Management and delivery are one system. Cloudinary Assets and the transformation and delivery layer share the same asset store. There is no synchronisation between the library and the thing serving images, because they are not separate things. Every platform in archetypes one to three has that seam, and the seam is where staleness, expiry propagation and takedown failures live.

    Metadata is typed and enforced at the API. Structured metadata fields carry types and validation applied on every write path, not only in the upload form. This is the property that determines whether your data quality survives integrations, which is where most assets arrive at enterprise scale.

    SDK breadth. Roughly seventeen languages and frameworks. You do not get to choose which stack the next consuming team writes in, and this is the difference between an integration that takes a week and one that starts with writing an HTTP client.

    Pricing is published. The tiers are listed rather than gated behind a sales call: free at 25 credits per month, Plus at 99 dollars per month for 225 credits, Advanced at 249 dollars per month for 600 credits, enterprise custom. A credit covers 1,000 transformations or 1 GB of storage or 1 GB of delivery, spent across those as you use them. In a category where almost nobody publishes a number, being able to model before you talk to anyone is worth more than it sounds.

    The onboarding path is machine-readable. MCP servers, an llms.txt and a transformation rules file mean an agent-assisted integration can produce correct code on the first attempt rather than plausible-looking wrong code. As more integration work becomes agent-assisted this stops being a curiosity, and it is a decent proxy for whether the API was designed to be read by something that has never seen it.

    Where the others win

    This is the section worth reading twice, because it is where the decision actually gets made.

    If your users live in the library all day, the brand library archetype has better interfaces. Bynder and Brandfolder are genuinely nicer to browse, collect and share in. If your primary population is five hundred regional marketers and agency staff who never touch an API, weight that heavily and do not let an architecture argument override it.

    If you need campaign planning, budgeting and approval routing in the same system, Aprimo does something the others do not attempt. Buying a DAM and then buying a workflow tool and integrating them is usually worse than buying the suite.

    If you have an existing enterprise content estate with records management and governance obligations, the content services platforms slot into it in a way that a media infrastructure platform does not. That integration work is real and it is not free.

    If you need only delivery, without a management layer, then imgix, ImageKit or Cloudflare Images are simpler and cheaper. Do not buy a DAM if what you have is a resizing problem. The honest version of that decision is in alternatives to a traditional enterprise DAM.

    If you have no engineering capacity at all, an excellent API is not an asset. A closed suite with pre-built connectors will serve you better than a superior platform you cannot call.

    Five off-white index cards in a row with different printed headers, two carrying cyan corner tabs, one turned out of alignment with an amber cross

    How to run the comparison

    Four steps, and none of them is a feature matrix.

    1. Write down who consumes assets and how. Count the humans who browse and the systems that call. That ratio picks your archetype before you look at a single vendor.

    2. Pick two archetypes, not five vendors. Then take the strongest one or two from each. Comparing across archetypes is where the interesting arguments happen; comparing within one is where the small differences are.

    3. Run the same technical test on each. Upload a photograph, request it at five widths in three formats by editing the URL, replace the master, confirm references update, and time each step. Half a day per vendor and it tells you more than any reference call.

    4. Model five years with all six cost lines. Licence, implementation, migration, storage, delivery and people, as set out in what enterprise DAM costs. The rankings on total cost frequently invert the rankings on licence price, and integration effort is the line that moves most between archetypes.

    Do that and the shortlist usually collapses to two, with a clear reason for each. Which is a much better position than four vendors at ninety-four percent on a scoring sheet nobody believes.

    Build the requirement list first from the requirements checklist, cut it before you send it, and use the business case to translate the result into a number finance will sign. If you are earlier than a shortlist, start with what enterprise DAM actually is.